Open Source keeps piling up —
if you've never checked the risks, now is the time.
Open Source keeps piling up —
if you've never checked the risks,now is the time.
From Log4j to React2Shell, see which open source components make up your code and where the risks are Only the first 100 sign-ups get 1 month of free access.
From Log4j to React2Shell,see which open source components make up your code and where the risks are Only the first 100 sign-ups get 1 month of free access.
Open source is open to everyone. If unmanaged, it's a cost to you.
No one builds software without open source anymore.
The problem is that most development teams don't actually know what open source components they're using.
And unmanaged open source becomes risk.
No one builds software without open source anymore.
The problem is that most development teams don't actually know what open source components they're using.
And unmanaged open source becomes risk.
License Compliance Risk
Violating the license terms set by copyright holders can lead to infringement lawsuits, service suspension, and other legal and business risks.
Rising Supply Chain Attacks
Supply chain attacks are a leading cause of global cyber threats. A single vulnerable component can affect an entire service and bring systems down.
Complex Dependency Structures
Beyond the libraries you use directly, hidden transitive dependencies also need to be managed.
Why is SBOM generation and management essential?
What is an SBOM (Software Bill of Materials)?
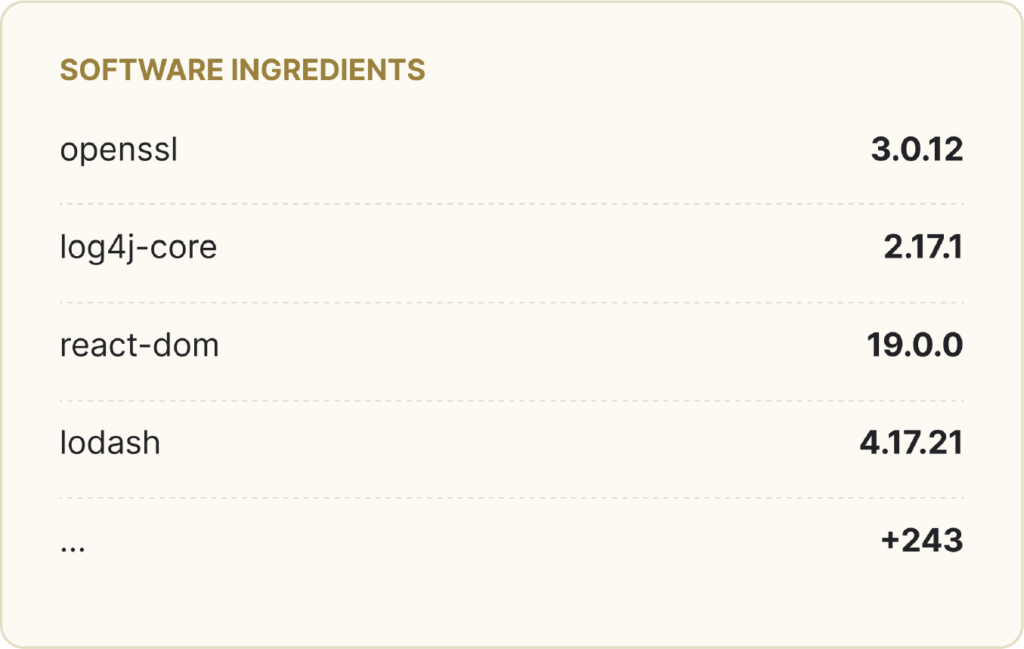
Also known as a software inventory, an SBOM is a file that lists information about the open source software contained in a given piece of software. Much like the ingredient label on the back of a food package, it transparently shows "what is included in the software, in which version, and how."
Why do you need an SBOM?
현Today, nearly 90% of software code depends on open source and third-party libraries. Even developers themselves find it hard to know which sub-libraries are hidden inside their own programs. More recently, beyond simply generating SBOMs, frameworks such as SLSA (Supply-chain Levels for Software Artifacts) are being used to prove software integrity and strengthen supply chain security. In other words, SBOMs serve as a means for software suppliers and consumers to share and continuously update information about the components included in the software.
Visibility into software components
Specifies every open source library and version included in your software, proving the trustworthiness of the entire supply chain.
Immediate tracking of new vulnerabilities
When a new security vulnerability (CVE) is disclosed, instantly identify which software contains the affected component and respond proactively.
Information included in an SBOM
Supplier name, component name, component version, unique identifier, dependency relationships, license and vulnerability information
SBOM Standard Data Format
SPDX · CycloneDX
Why is SBOM generation and management essential?
What is an SBOM (Software Bill of Materials)?
Also known as a software inventory, an SBOM is a file that lists information about the open source software contained in a given piece of software. Much like the ingredient label on the back of a food package, it transparently shows "what is included in the software, in which version, and how."
Why do you need an SBOM?
현Today, nearly 90% of software code depends on open source and third-party libraries. Even developers themselves find it hard to know which sub-libraries are hidden inside their own programs. More recently, beyond simply generating SBOMs, frameworks such as SLSA (Supply-chain Levels for Software Artifacts) are being used to prove software integrity and strengthen supply chain security. In other words, SBOMs serve as a means for software suppliers and consumers to share and continuously update information about the components included in the software.
Visibility into software components
Specifies every open source library and version included in your software, proving the trustworthiness of the entire supply chain.
Immediate tracking of new vulnerabilities
When a new security vulnerability (CVE) is disclosed, instantly identify which software contains the affected component and respond proactively.
Information included in an SBOM
Supplier name, component name, component version, unique identifier, dependency relationships, license and vulnerability information
SBOM Standard Data Format
SPDX · CycloneDX
Diagnosing Risk and Building an Inventory Are Two Different Jobs
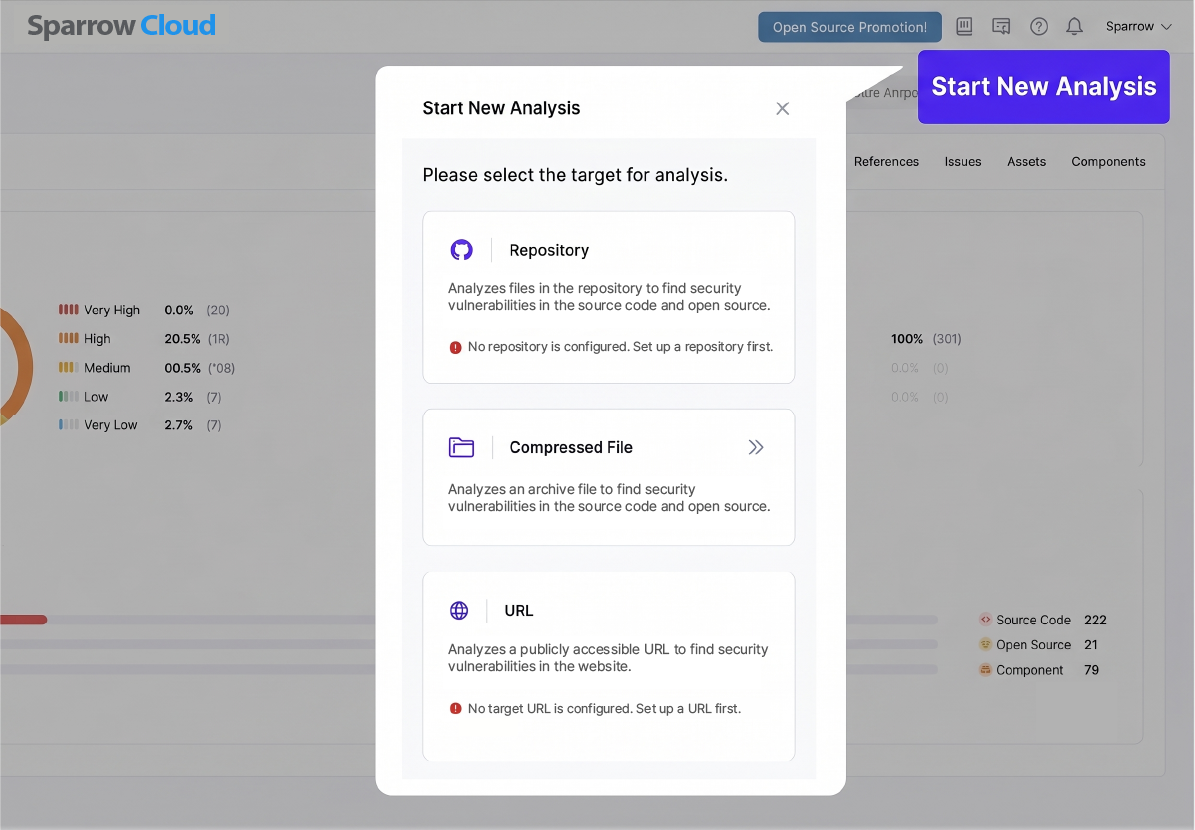
Sparrow SCA: Automatic identification of open source licenses and vulnerabilities
Automatically detects the open source components and licenses in use, and delivers vulnerability information alongside the notice obligations for each license.
A new SBOM is generated every time your software is updated. How are you managing them? Without a dedicated platform, managing SBOMs individually makes it difficult to systematically track version change history — and when a new vulnerability emerges, it's hard to immediately identify which SBOM versions are affected.
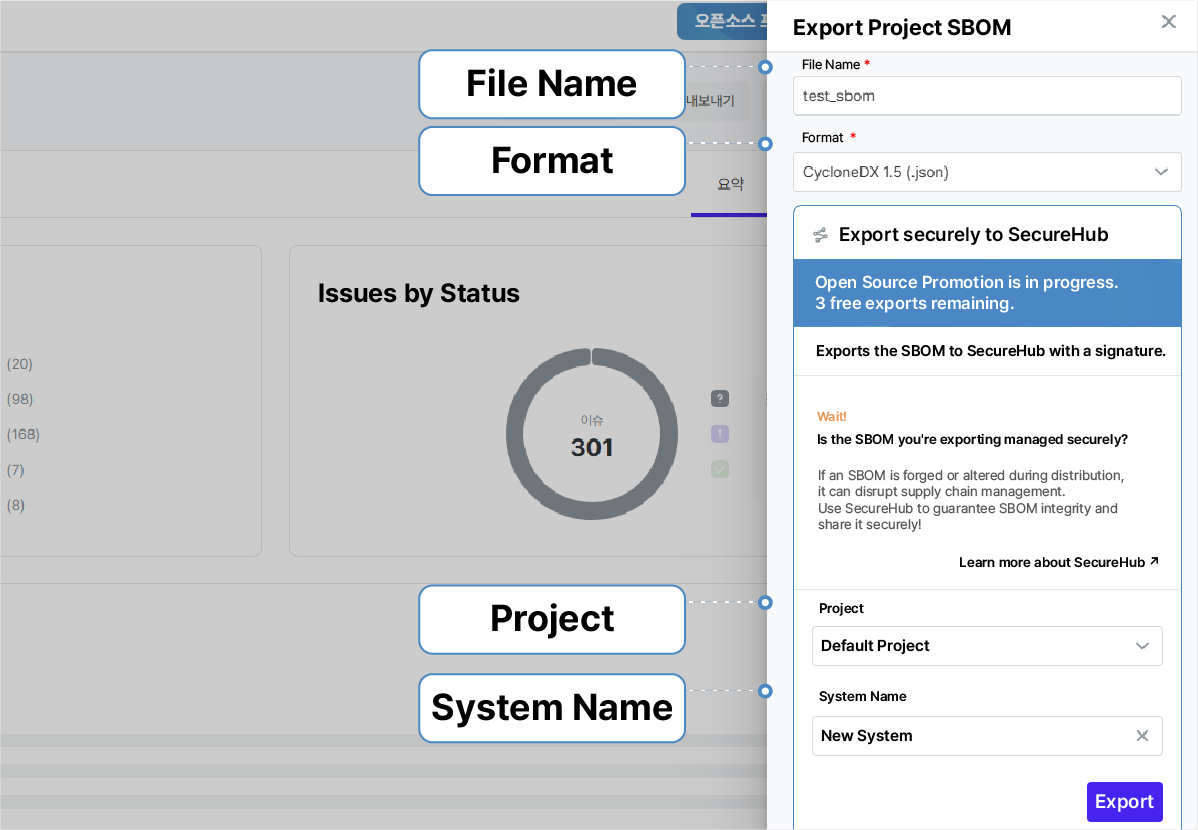
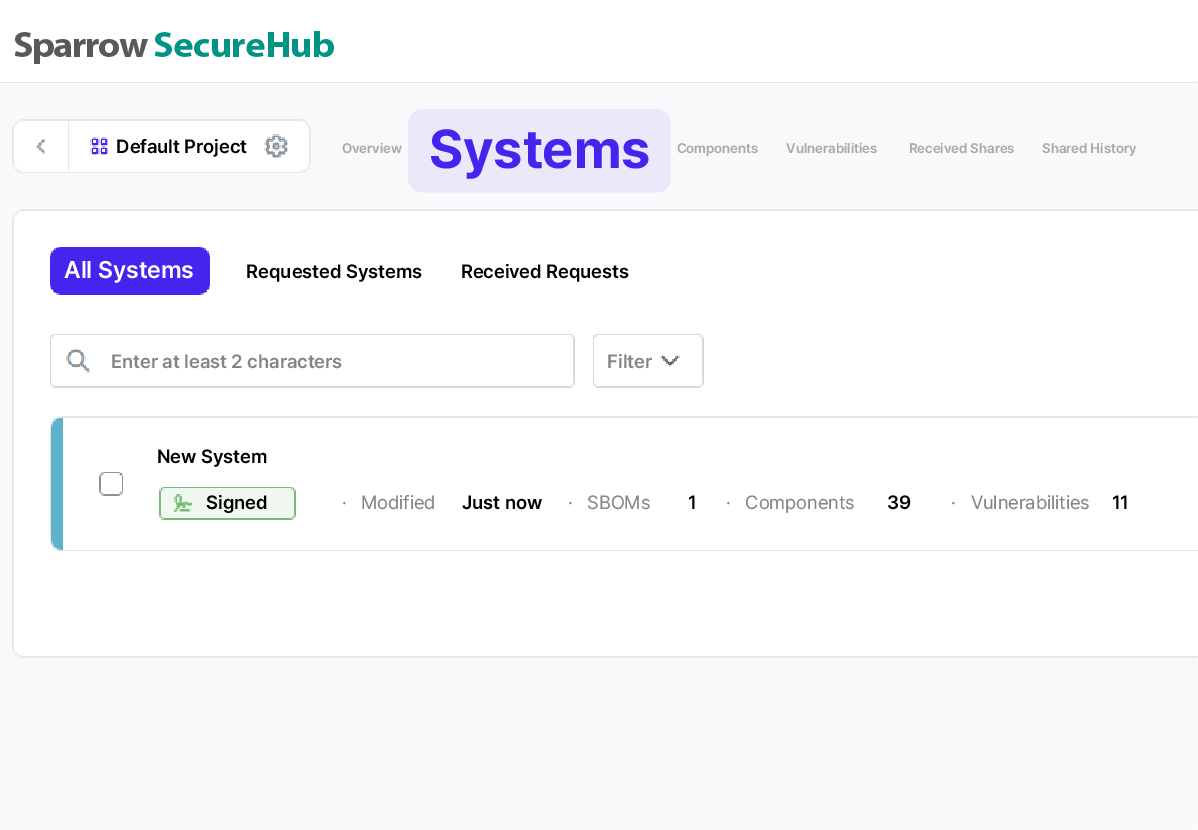
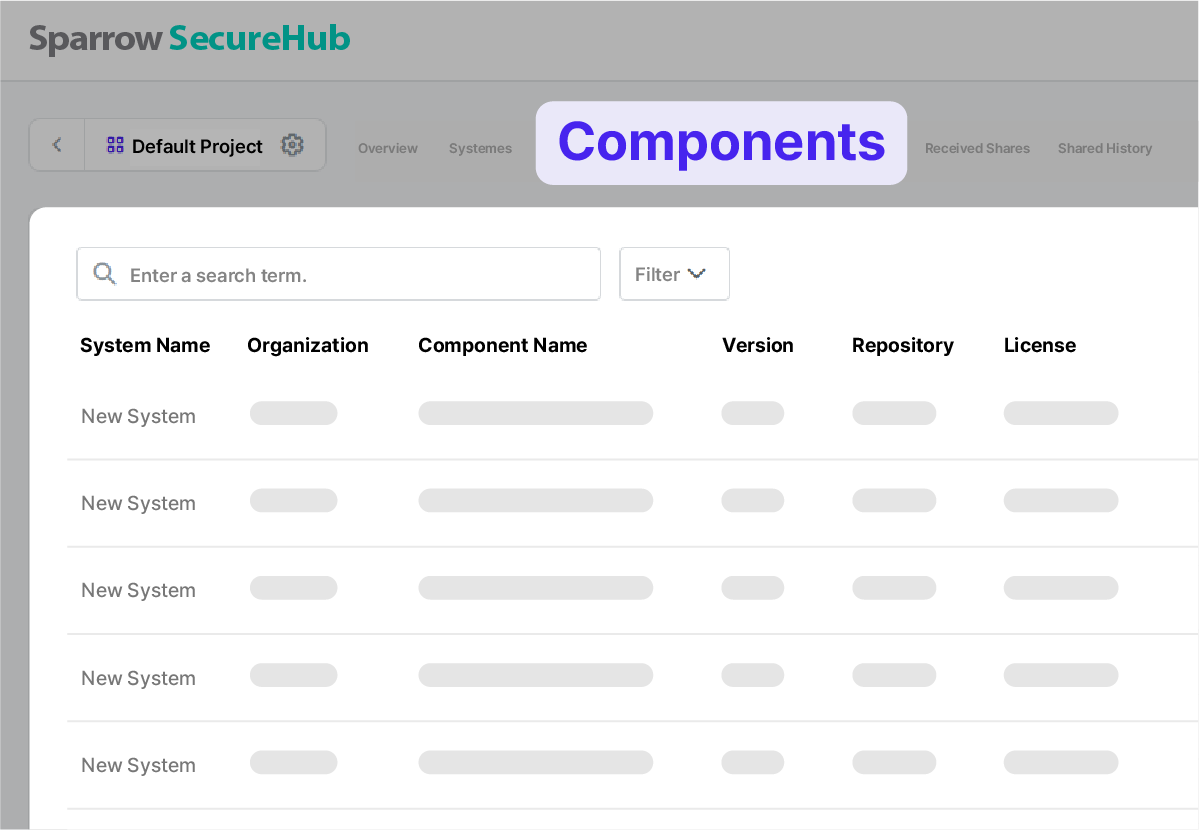
Sparrow SecureHub provides a management framework that gives you a clear view of SBOM generation and sharing history along with all changes. In addition to digital-signature-based integrity verification, it instantly identifies the components affected by newly disclosed vulnerabilities, enabling even organizations without dedicated security staff to respond to supply chain security quickly and systematically.
Diagnosing Risk and Building an Inventory Are Two Different Jobs
Sparrow SCA: Automatic identification of open source licenses and vulnerabilities
Automatically detects the open source components and licenses in use, and delivers vulnerability information alongside the notice obligations for each license.
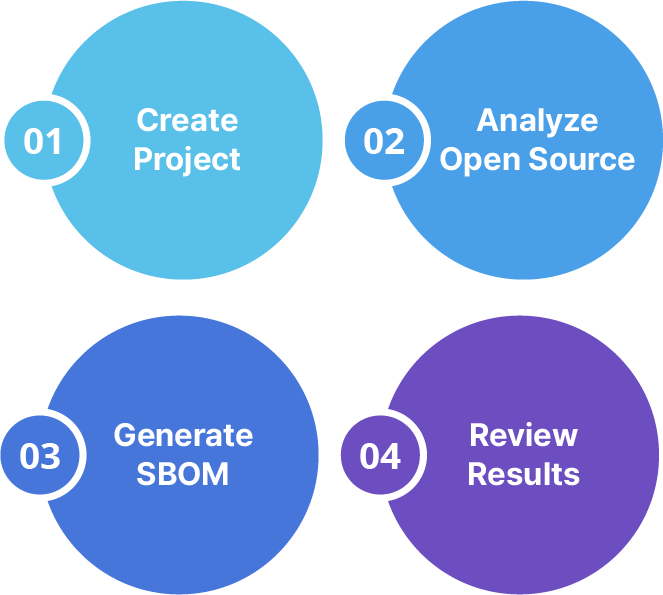
Generates SBOMs in international standard formats with a single click, and lets you securely share and distribute them with guaranteed integrity.
Wait, a quick note!
What is Sparrow SecureHub?
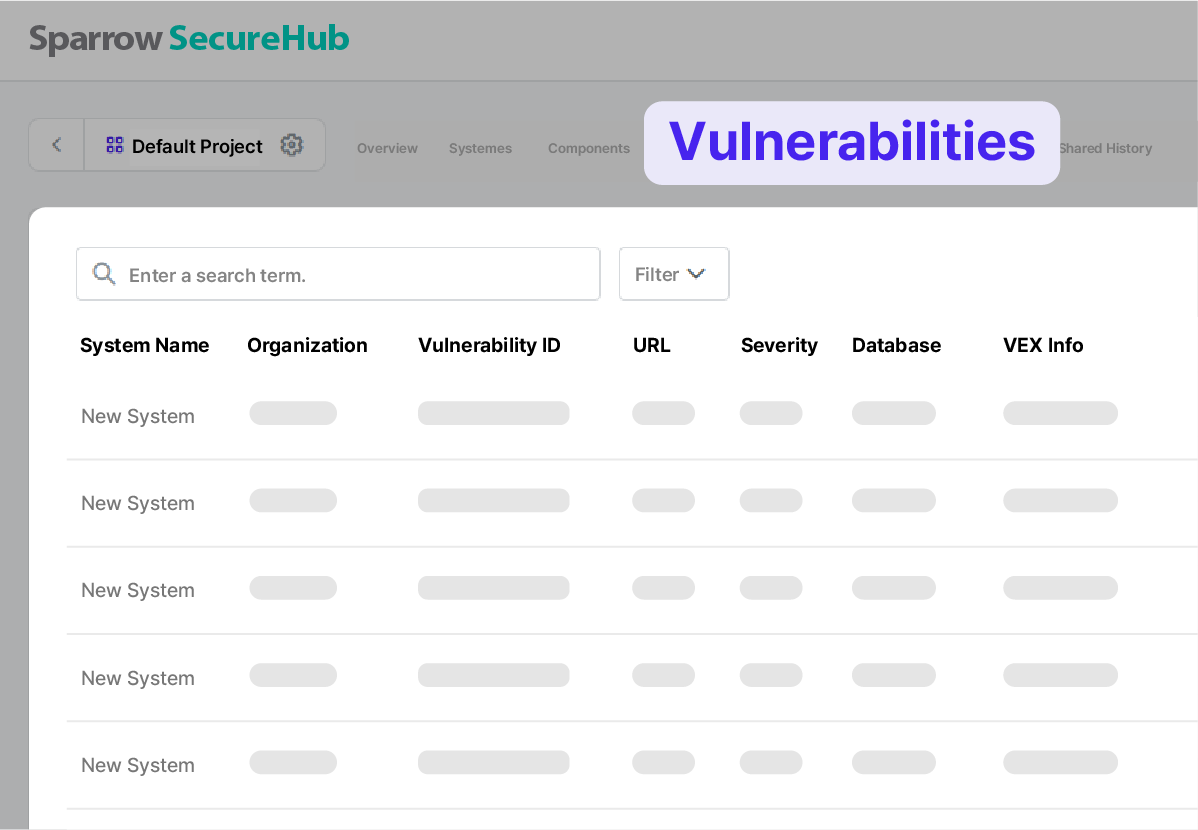
A service that lets you register, sign, and share SBOMs, and view the system, component, and vulnerability information they contain.
A new SBOM is generated every time your software is updated. How are you managing them? Without a dedicated platform, managing SBOMs individually makes it difficult to systematically track version change history — and when a new vulnerability emerges, it's hard to immediately identify which SBOM versions are affected.
Sparrow SecureHub provides a management framework that gives you a clear view of SBOM generation and sharing history along with all changes. In addition to digital-signature-based integrity verification, it instantly identifies the components affected by newly disclosed vulnerabilities, enabling even organizations without dedicated security staff to respond to supply chain security quickly and systematically.